How alarms helped protect plasma in the French blood-service cyber incident
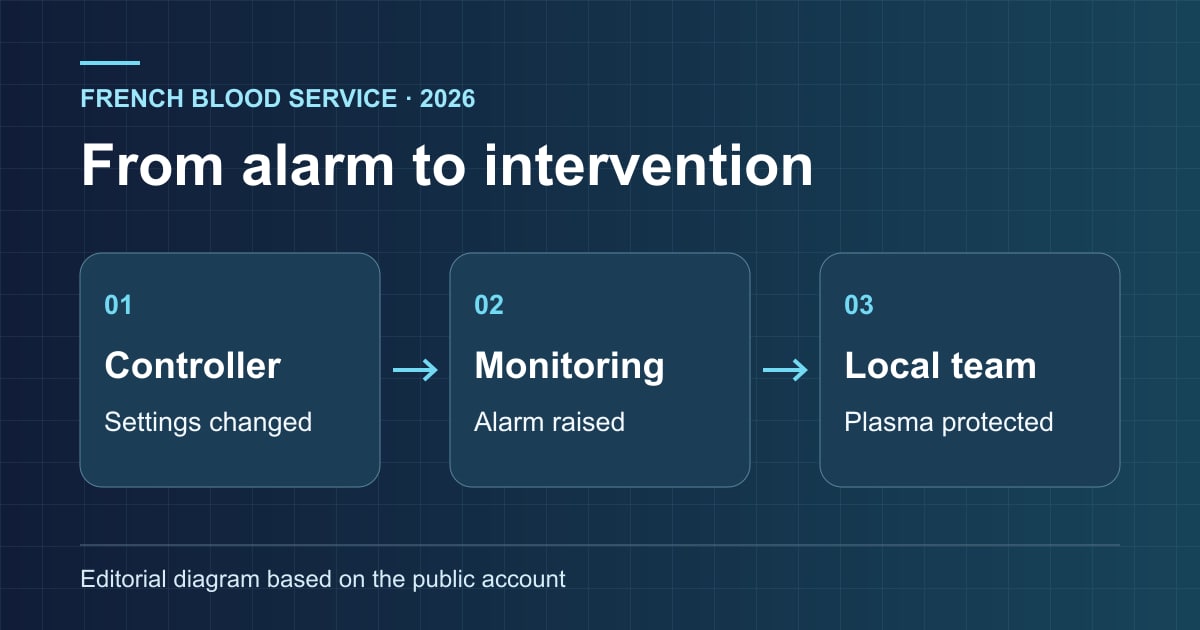
A supplier-related attack altered refrigeration controls at three EFS sites. Monitoring gave staff time to protect the products and keep distribution running.
ASSURED DIGITAL / INSIGHTS & RESOURCES
Fresh perspectives and practical tools for the decisions ahead.
Cyber resilience
Turn security questions into clear controls, evidence and recovery decisions.
Find a perspective. Preview it. Put it to work.
23 resultsLatest first
A supplier-related attack altered refrigeration controls at three EFS sites. Monitoring gave staff time to protect the products and keep distribution running.
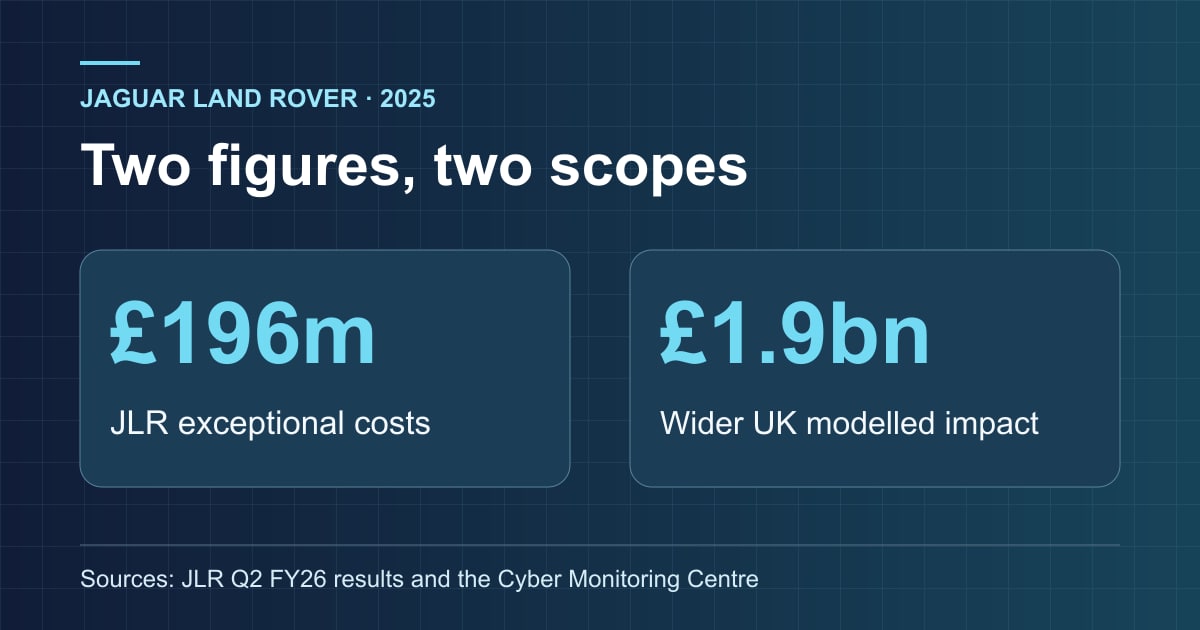
JLR reported £196m of cyber-related exceptional costs. The CMC estimated £1.9bn across the UK. The distinction changes how leaders should read the case.
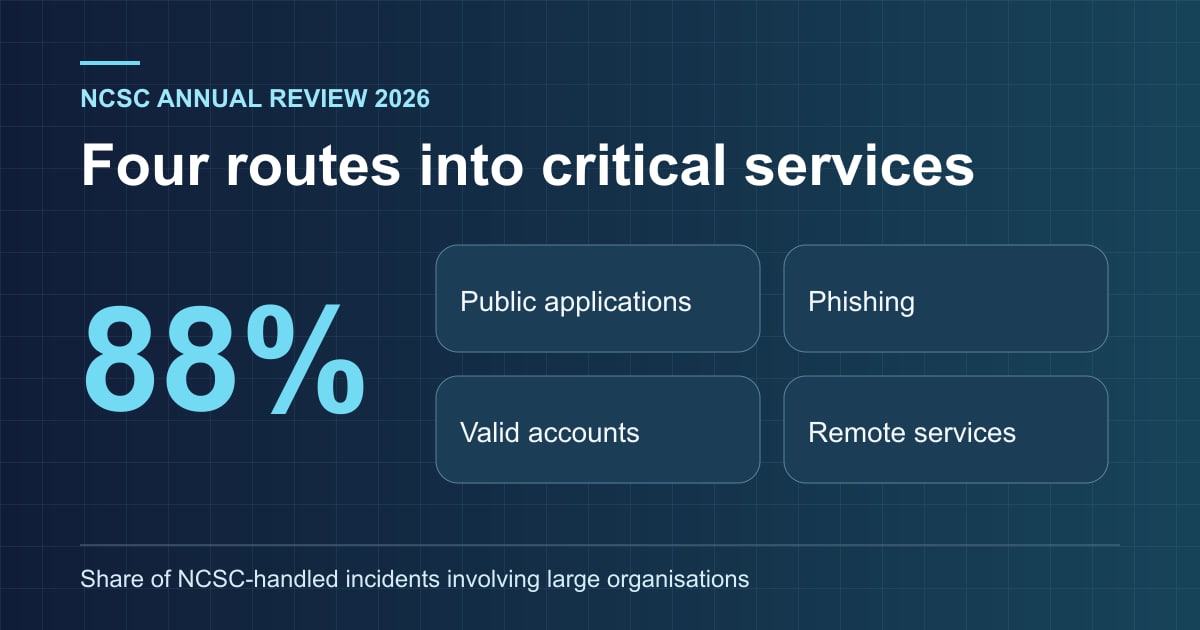
Four established entry routes still matter. AI changes how fast attackers can find and exploit them, and how defenders should prioritise their response.
A construction IT guide to choosing between managed company phones, protected work apps on personal devices and narrower project access. With the checks to make before rollout.
Map the accounts, applications and providers behind one critical activity, and agree what the team can safely do while a service is unavailable.
When a message asks for a new sign-in, wider access or an urgent change, give the team a clear way to verify it.
How HSEQ, governance and IT colleagues can build a clear answer about work phones and subcontractor access, backed by a record of what actually happened.
DSPT Version 9 is the 2026–27 Toolkit cycle, aligned to CAF 4.0, with the submission deadline set for 30 June 2027. For established suppliers, the important job is checking whether last year's answers still match today's environment.
The NHS Cyber Security Charter is a useful public commitment, but the interesting bit starts after the signature. Can the supplier show that the commitments are actually working in the business?
The Stryker attack showed how supplier disruption can hit NHS delivery. Learn how to map dependencies, test recovery and reduce single-point-of-failure risk.
Employee BYOD, subcontractors’ own phones and the accounts your business provides are treated differently. Here is how to work through the current scope rules with IT.
Third-party cyber risk is no longer a niche concern. The recent Rockstar incident shows how attackers are exploiting trusted relationships, not just breaking through the perimeter, and what UK organisations need to do about it.